Mortgage Industry Cybersecurity: What Lenders Need to Know Now


Updated September 10, 2026
Mortgage industry cybersecurity has become one of the most urgent operational challenges facing lenders today. Every dollar of fraud loss cost lenders $4.40 in fines, legal fees, labor, and recovery expenses through the first three quarters of 2021, according to LexisNexis Risk Solutions. Firms reported a monthly average of 1,431 fraud attempts that same year. And the threat has only grown more sophisticated since then, with AI-generated deepfakes, synthetic identities, and business email compromise now targeting the same workflows that lenders have spent years digitizing.
The mortgage industry is more exposed to fraud than banks and other financial services sectors, according to LexisNexis. Threats occur at every stage of the process, from account creation and loan application through funds distribution and closing. Acquiring housing through fraudulent activity was involved in five of the top six threats LexisNexis identified. Yet a significant share of mortgage leaders still admit they are not taking the precautions the risk environment demands.
This article breaks down why the mortgage industry is a prime target, what the regulatory landscape requires, which threats are most active, and what a defensible cybersecurity program actually looks like.
Key takeaways
- Every dollar of mortgage fraud loss costs lenders $4.40 in total recovery expenses, including fines, legal fees, and labor.
- The mortgage industry faces more fraud exposure than banks and other financial services sectors, with threats spanning every stage of the lending lifecycle.
- Spear phishing and business email compromise are the most common attack vectors, with 49% of banking and mortgage leaders identifying them as top threats.
- The FTC Safeguards Rule, GLBA, and state regulations like NYDFS 23 NYCRR Part 500 impose specific, enforceable cybersecurity requirements on mortgage firms, including breach notification windows as short as 48 hours.
- AI-generated fraud, including deepfakes and synthetic identities, is now targeting mortgage transactions at closing, a threat most cybersecurity programs were not designed to stop.
- Identity verification at the point of signing and wire authorization is a control that closes gaps that endpoint security and multi-factor authentication alone cannot address.
Why the mortgage industry is a prime target for cyberattacks
The mortgage industry sits at the intersection of financial, privacy, and cyber risk. Mortgage firms collect tax returns, bank statements, credit reports, and government-issued identification from every borrower. That data is valuable. The transactions are time-sensitive. And the closing process involves large wire transfers that, once sent, are nearly impossible to reverse.
Attackers understand this calculus better than most lenders do. The financial sector's built-in reliance on rapid transaction processing plays directly into threat actors' objectives. Time pressure creates urgency, and urgency creates mistakes. A borrower who receives a fraudulent wire instruction 48 hours before closing is under enormous pressure to act fast.
Most mortgage firms also rely on third-party technology, including loan origination systems, title production software, and mobile platforms they did not build themselves. That creates a supply chain of potential vulnerabilities. When a vendor's software is not patched, threat actors can exploit it across every firm using that platform. The Apache Log4j vulnerability, discovered in December 2021, illustrated exactly this risk: a single flaw in widely used software threatened the lending platforms of thousands of institutions simultaneously.
The AI fraud threat that most programs are not built to stop
The threat landscape has shifted materially since 2022. Generative AI now enables attackers to produce synthetic identities, deepfake video, and forged documents at a scale and speed that traditional verification controls were not designed to detect.
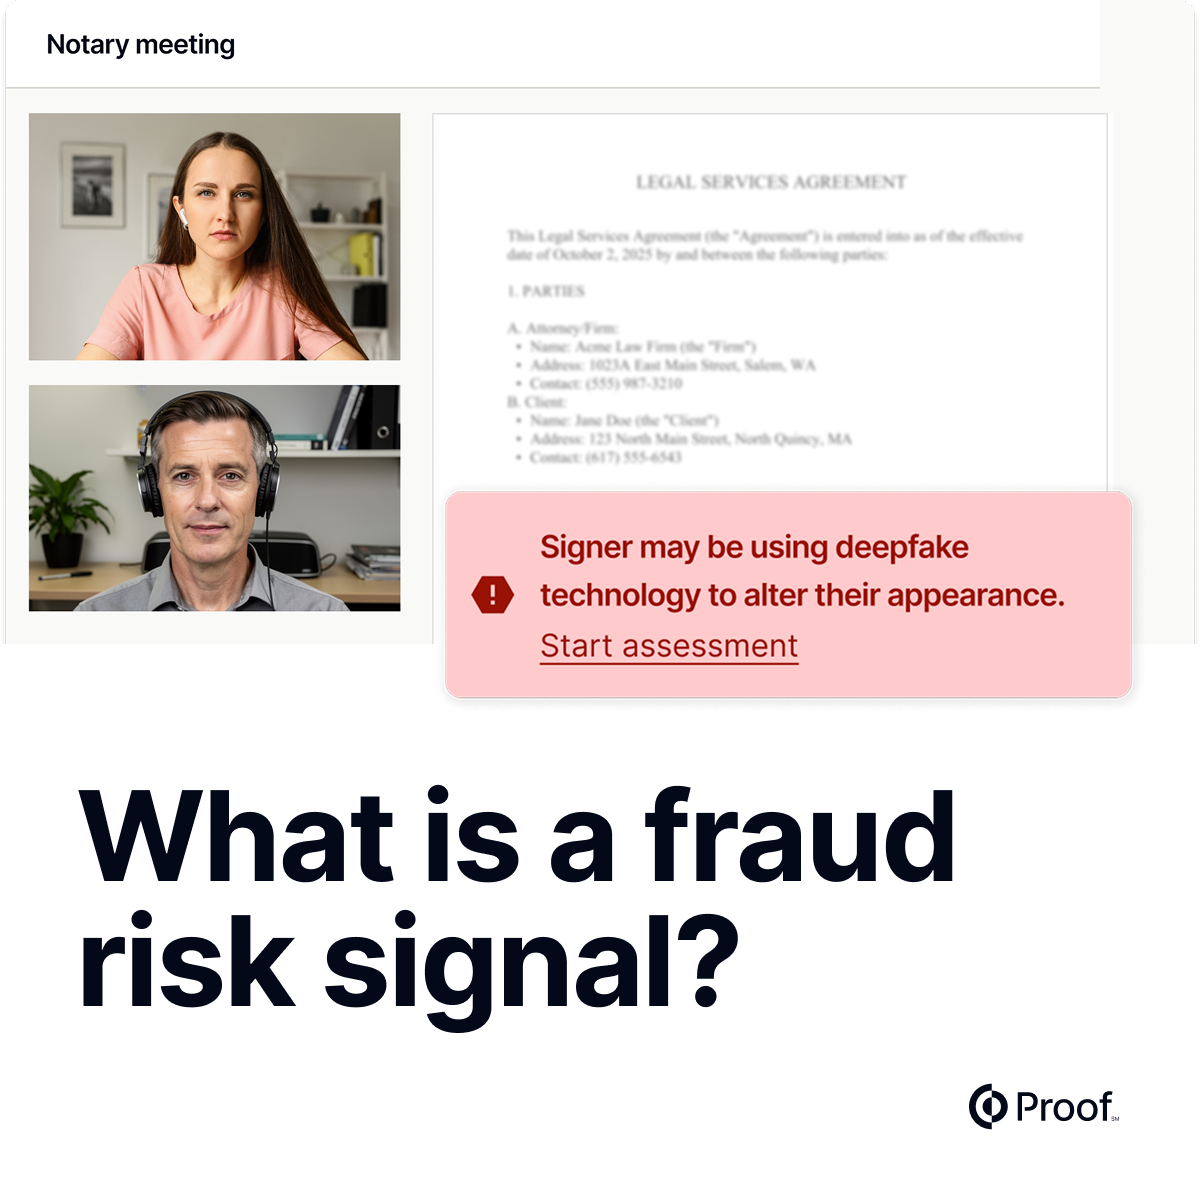
A borrower who appears on a video call may be a deepfake. A government-issued ID submitted for verification may be AI-generated. A wire authorization request may come from a compromised email account controlled by a threat actor who has been reading every message for months. One cybersecurity expert estimated that 10% of small mortgage brokerages have at least one employee with a compromised email account, often without knowing it.
These are not hypothetical risks. They are active attack patterns targeting the same digital workflows that lenders have invested in to improve efficiency.
The regulatory landscape: what mortgage firms must comply with
Mortgage companies are financial institutions under federal law, which means they carry a specific set of cybersecurity obligations. The regulatory framework is not optional, and the consequences of non-compliance are concrete.
Key regulations that apply to mortgage lenders
- Gramm-Leach-Bliley Act (GLBA) Safeguards Rule: Requires financial institutions to design, implement, and maintain a written information security program protecting customer data. The FTC updated the rule in 2021 to reflect current technology, adding requirements for risk assessments, encryption, multi-factor authentication (MFA), and ongoing monitoring.
- FTC Safeguards Rule (updated 2023): Enforces specific technical controls and carries fines of up to $46,517 per consent order violation. The rule requires firms to designate a qualified individual to oversee the information security program and report to the board at least annually.
- New York Department of Financial Services (NYDFS) 23 NYCRR Part 500: Requires annual attestations of cybersecurity protocols and mandates breach notification. Failure to notify regulators incurs fines and possible loss of licensure.
- Ginnie Mae breach notification: Ginnie Mae has instituted a 48-hour breach notification window, the shortest of any federal mortgage regulator. Most mortgage companies lack the infrastructure to detect, diagnose, and report a breach that quickly.
- Fannie Mae and Freddie Mac data protection requirements: Mandate secure data handling for all participating lenders and servicers.
- State privacy regulations: A patchwork of state laws, including California Consumer Privacy Act (CCPA) and various state breach notification statutes, impose additional obligations that vary by jurisdiction.
The compliance pressure is also coming from cyber insurance carriers. Garry Woods, executive director of governance, risk, compliance, and policy for cybersecurity firm Richey May, noted that mortgage firms may be forced to improve their security posture by their insurers, not just their regulators. Cyber insurance premiums are rising, and carriers are demanding evidence of specific controls before they will renew coverage.
The threats mortgage companies face daily
Mortgage industry cybersecurity threats are not abstract. They are operational events that delay closings, expose borrower data, and generate recovery costs that dwarf the original fraud loss.
Business email compromise and wire fraud
Spear phishing is the most common attack vector in the mortgage industry. Forty-nine percent of banking and mortgage leaders identified it as one of their greatest cybersecurity threats, according to an Arizent survey. The attack pattern is straightforward: a threat actor gains access to an email account, monitors correspondence, and then sends a fraudulent wire instruction to a borrower or closing agent at the moment of maximum urgency.
One documented case involved a borrower who wired $190,000 to a criminal posing as a title company. The borrower was not unsophisticated. The attack worked because the fraudulent email arrived at exactly the right moment in the transaction and appeared to come from a trusted source.
Ransomware and data breaches
Ransomware attacks against major mortgage servicers made headlines in late 2023 and early 2024. Mr. Cooper Group, Fidelity National Financial, First American Financial, and loanDepot were all hit within a matter of months. The attacks compromised sensitive corporate and customer data, delayed closing times on new loans, and prevented customers from making payments.
These were not isolated incidents. They reflect a pattern of opportunistic attacks against an industry that handles enormous volumes of sensitive financial data and operates under time pressure that makes downtime especially costly.
Fifty-one percent of banking and mortgage respondents in the Arizent survey identified data breaches as one of their greatest concerns. Insider threats, including employees taking proprietary information when they leave, compound the risk.
Bot attacks and online application fraud
Companies that allow online loan applications face a growing volume of bot attacks. Only 31% of Arizent respondents identified bot attacks as a near-term risk, suggesting the industry is underestimating this threat. Automated attacks can probe application systems for vulnerabilities, harvest data, and submit fraudulent applications at scale.
Deepfakes, synthetic identities, and AI-generated fraud
This is the threat that most mortgage cybersecurity programs were not designed to address. AI tools now make it possible to generate convincing fake IDs, synthetic identities that pass standard database checks, and deepfake video that can fool visual verification. As lenders adopt remote online notarization (RON) and digital closing workflows, the attack surface for these techniques expands.
Standard identity verification that relies on document capture and database matching is no longer sufficient against AI-generated fraud. Liveness detection, biometric comparison, and cryptographically signed records are now necessary components of a defensible verification stack.
Cyber risk is business risk: the real cost of a breach
Mortgage industry cybersecurity is a business problem, not just an IT problem. The financial impact of a breach extends well beyond the initial fraud loss.
Every dollar of fraud loss cost lenders $4.40 in total recovery expenses through the first three quarters of 2021. That multiplier includes fines, legal fees, labor, and related costs. A ransomware attack that takes a lender's systems offline for even a few days can generate millions in lost revenue, operational disruption, and reputational damage.
The regulatory consequences are equally concrete. A mortgage company operating in New York that fails to notify NYDFS of a breach faces fines and possible loss of licensure. A company that cannot demonstrate compliance with the FTC Safeguards Rule faces fines of up to $46,517 per violation. And a company that cannot produce a written incident response plan when its cyber insurance carrier asks for one at renewal may find itself uninsurable.
Borrower trust is also at stake. When sensitive financial data is compromised, the consequences extend to delays in loan settlements, breaches of client confidentiality, and reputational damage that takes years to rebuild. In an industry built on trust, a single incident can cost a lender relationships that took decades to develop.
How to build a defensible mortgage cybersecurity program
The FTC Safeguards Rule provides a useful framework for what a defensible program must include. Mortgage firms that structure their security posture around these nine elements will satisfy most regulatory requirements and significantly reduce their exposure.
The nine elements of the FTC Safeguards Rule
- Designate a qualified individual to implement and supervise the information security program.
- Conduct a written risk assessment with criteria for evaluating identified risks and threats.
- Design and implement safeguards to control identified risks, including access controls, encryption, MFA, and secure data disposal.
- Regularly monitor and test the effectiveness of safeguards through continuous monitoring or annual penetration testing.
- Train staff on security risks and their responsibilities.
- Monitor service providers and enforce security expectations through contracts.
- Keep the information security program current as operations and threats evolve.
- Create a written incident response plan with defined roles, communication protocols, and post-incident review procedures.
- Require the qualified individual to report to the board or senior leadership in writing at least annually.
Only 54% of banking and mortgage respondents in the Arizent survey said their organization practices periodic data breach simulations. Only 47% said their firms routinely attempt to penetrate their own IT infrastructure. Those numbers need to be higher, and the regulatory and insurance pressure to improve them is building.
Identity verification as a security control
Most cybersecurity programs focus on network security, endpoint protection, and employee training. Those controls matter. But they do not address the identity layer, specifically the question of whether the person signing a document, authorizing a wire, or completing a closing is actually who they claim to be.
Identity verification at the point of signing and wire authorization closes a gap that MFA and encryption cannot. A borrower who receives a wire instruction and calls to confirm it can still be deceived if the phone number they call has been spoofed. A notary who conducts a video session can still be fooled by a deepfake if the platform does not run liveness detection and biometric comparison.
Proof's Identify product runs 25 identity checks in under five seconds, combining credential analysis, biometric comparison, and liveness detection. When automated checks flag a risk, the workflow escalates to a live trusted fraud agent for review. The outcome is a detailed identity report that documents verification results and risk indicators, creating a durable record that satisfies both regulatory and insurance requirements.
Third-party and vendor risk management
Third-party risk is one of the two largest threats facing the mortgage industry, alongside the human element, according to cybersecurity experts. A mortgage company can be liable if a third-party provider is breached, even if the breach was not the lender's fault. Regulators like Ginnie Mae and NYDFS impose their standards on mortgage companies' third-party providers.
A defensible vendor risk program includes:
- Written contracts that specify security expectations and audit rights
- Periodic reassessments of vendor security posture
- Inventory of all third-party systems that access or store borrower data
- Incident response coordination procedures that include vendors
Penetration testing and breach simulations
Simple actions like resetting passwords and requiring MFA can mitigate 80 to 90% of attacks, according to security experts who work with small mortgage brokerages. But firms also need to test whether those controls actually work. Annual penetration testing and periodic breach simulations are now requirements under the FTC Safeguards Rule, and they are increasingly required by cyber insurance carriers as a condition of coverage.
What mortgage lenders should do now
The gap between awareness and action in mortgage industry cybersecurity is closing, but too slowly. Regulatory pressure, insurance requirements, and the rising cost of fraud are all pushing lenders toward stronger security postures. The firms that move first will be better positioned to satisfy examiner requirements, retain cyber insurance at reasonable premiums, and protect borrower relationships.
The most important steps are:
- Designate a qualified individual to own the information security program and report to leadership
- Conduct a written risk assessment that covers all systems, vendors, and data flows
- Implement MFA across all systems that access borrower data
- Establish a written incident response plan before an incident occurs
- Add identity verification at the point of signing and wire authorization, not just at onboarding
- Test your controls through penetration testing and breach simulations at least annually
- Review all third-party vendor contracts for security requirements and audit rights
The mortgage industry's digital transformation is not slowing down. Every new digital workflow, mobile platform, and third-party integration expands the attack surface. The firms that treat cybersecurity as a business risk, and fund it accordingly, are the ones that will close loans faster, satisfy regulators, and protect the borrowers who trust them with their most sensitive financial information.
See how Proof Identify secures mortgage transactions with IAL2-certified identity verification.